Answer six, see your gaps
The same opening conversation we have with every client, in the same order. Answers stay in your browser until you choose to send them.
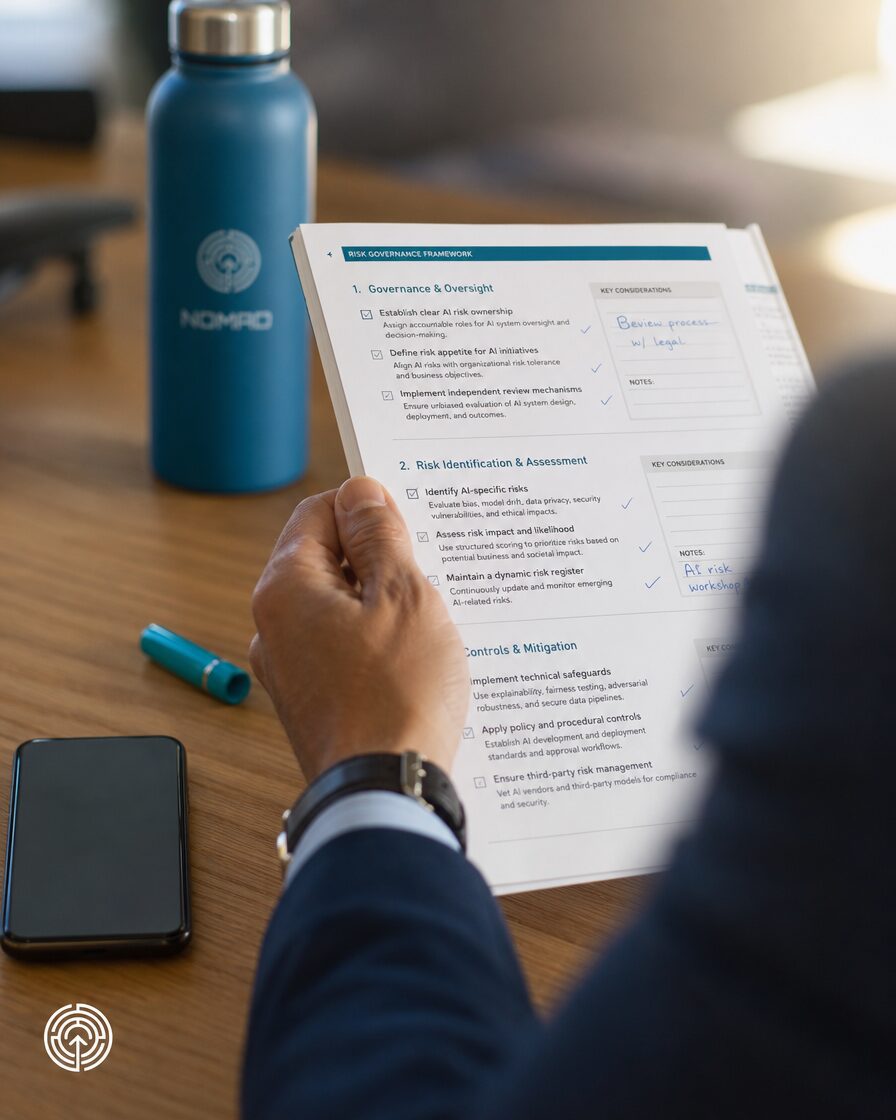
Scoring is deliberately blunt: two points where something is standing and owned, one where it exists but is informal, none where it does not exist yet.
Do you know everywhere AI is being used across the business?
Is one person accountable for AI risk decisions?
Are your AI and data policies written and approved?
Could you answer a client or auditor questionnaire this week?
Do you review AI vendors and third-party models before use?
Is anyone tracking which AI rules apply to you as they change?
There is no program to point to yet
A client questionnaire or an auditor would find nothing standing. Start at Crawl: scope, ownership, and a gap map before any spend.
Pieces exist, but the seams show
You could answer some questions and not others, which is where incidents live. Start at Walk: formalize policy and get evidence collecting itself.
You can show your work
The foundation holds. Start at Run: validate controls, close the remaining gaps, and keep pace as rules and models change.
Request an exposure review
An advisor reviews your cyber and AI governance posture against the obligations enforceable today and returns a red, yellow, green picture of what to address first.
No obligation, and you keep the findings either way. We reply within one business day.