Your AI is moving faster than your oversight.
Nomad builds AI and cyber governance for mid-market organizations that carry enterprise obligations without an enterprise compliance function. We build it, then stay while it holds.
The advisor already in the room
Nomad Cyber Concepts is an AI governance and cyber risk advisory firm founded in 2023 and based in Grapevine, Texas. We work inside your organization rather than across a table from it: in your meetings, on your tools, accountable for the same outcomes your team is.
Our advisors have carried this work in regulated environments and Fortune 100 and 500 environments before. They speak to IT, legal, and the boardroom in the language each one uses, and they say plainly what is enforceable now and what is only direction of travel.
Enterprises have compliance departments. You have the same obligations.
AI went into hiring, operations, client analytics and product decisions faster than oversight could keep up. Four things follow from that, and all four land on the same small team.
Obligations arrive by law
Texas, California, Colorado, Utah, the EU AI Act and the state wave behind them reach companies of every size. TRAIGA even reaches systems deployed before it took effect.
And by contract, sooner
Enterprise customers, insurers and acquirers already ask AI governance questions in vendor reviews, renewals and diligence. Contract arrives before statute.
The capability is not in-house
No model risk team, and no appetite to build one. AI risk sits between IT, legal and the business, owned by no one.
The work does not end
Models change, vendors change, rules move. A policy written last year cannot answer this year’s regulation or client questionnaire, so governance is a standing requirement rather than a project.
Liability follows the organization that uses the AI, not just the vendor that built it.
In Mobley v. Workday, a federal court allowed a nationwide collective action to proceed over AI-driven hiring screens. “The tool did it” is not a defense.
Three practices, one relationship
AI governance · Cyber risk · Professional developmentEvery engagement is fitted to your needs, targets and budget. Pick a practice to see what that covers.
AI Governance
Frameworks, policy, and oversight for the AI already inside your operations. We settle who owns which decision, then build the evidence trail that proves it.
Cyber Risk & Compliance
GRC advisory and audit readiness for teams without a compliance function. We find the exposure, then put controls and evidence behind it.
Professional Development
Business strategy and enablement, because counsel that never reaches the team does not hold. We teach the people who have to live with the controls.
Still confused about AI governance?
Three ways to say itThe term gets used loosely, so here it is plainly, then in the words of two of the vendors your enterprise customers already rely on.
It is the rulebook for how your organization uses AI
Governance is how decisions get made, who is accountable for them, and how you prove it later. Applied to AI, it answers three questions any board member, customer or regulator can ask you today.
If you cannot answer those three, you do not have AI governance yet. You have AI.
The definitions agree on what good looks like. The gap for mid-market organizations is that the platforms assume a compliance function you may not have. We build the policy, the inventory, the review gates and the evidence trail, then train your people to run them.
Request an assessmentGuardrails around the tools
“AI governance refers to the guardrails that help ensure AI tools and systems remain safe, ethical and respect human rights.”
IBM frames those three as the outcomes effective governance delivers.
Source · IBM · What is AI governance?The definitions agree on what good looks like. The gap for mid-market organizations is that the platforms assume a compliance function you may not have. We build the policy, the inventory, the review gates and the evidence trail, then train your people to run them.
Request an assessmentControls across the AI lifecycle
“AI governance is the policies, processes, and controls to manage AI risk, performance, and compliance across the AI lifecycle.”
OneTrust describes it as a management framework, not a one-time review.
Source · OneTrust · AI governance glossaryThe definitions agree on what good looks like. The gap for mid-market organizations is that the platforms assume a compliance function you may not have. We build the policy, the inventory, the review gates and the evidence trail, then train your people to run them.
Request an assessmentHow engagements are shaped
Enter anywhereMost clients start with a conversation or an assessment, then decide how far to go. Nothing here requires committing to a program first.
Find out where you stand
Short, scoped, and useful on its own.
Stand the program up
Scoped to your environment, your team, and your budget.
Keep it holding
For teams that need the program maintained, not handed over.
Pick where you operate
We tier obligations honestly: what is enforceable now, and what is direction of travel. Select your markets to see which is which.
Nothing selected yet. Most mid-market clients start with Texas, their enterprise customers, or both.
In force, with penalties up to $200K per violation, and it reaches AI systems that were already deployed before it took effect. There is no grandfather clause to wait behind.
Automated decision-making technology rules in force alongside TRAIGA, binding companies that make consequential decisions about Californians.
Operative this year, adding disclosure duties on top of the ADMT rules for organizations serving the California market.
The earliest of the state laws and a useful precedent: obligations arrived quietly and applied to companies of every size.
Transparency obligations in force for AI that interacts with people or generates content, reaching U.S. firms that serve EU markets.
Contract arrives before statute. AI governance questions already appear in vendor reviews, renewals and diligence, with NIST AI RMF and ISO/IEC 42001 converging as the evidence baseline.
Moved from June 2026. Duties for developers and deployers of high-risk AI systems, narrowed but not withdrawn.
New prohibitions take hold and legacy transparency duties attach to systems already on the market.
Moved from August 2026. The rescheduling reduced none of the obligations, only the date.
Moved from August 2027. Product-embedded high-risk systems come into scope last.
Crawl, walk, run
Three phases, paced to your budget and your people. Most organizations reach a governed program in three to six months. Click a phase.
Foundational readiness
We start with a conversation rather than a questionnaire, then agree scope and ownership and find the gaps across security, process, and controls.
Take the readiness check
Six questions, two minutes, and a red, amber or green answer with the gaps we would look at first. Nothing is sent until you decide to send it.
Start the checkControl implementation
Policies become formal, controls go in, and evidence collection starts running on its own schedule rather than yours.
Take the readiness check
Six questions, two minutes, and a red, amber or green answer with the gaps we would look at first. Nothing is sent until you decide to send it.
Start the checkAudit and proof readiness
Controls validated, gaps remediated, and your team ready for auditors, clients, and regulators without a scramble.
Take the readiness check
Six questions, two minutes, and a red, amber or green answer with the gaps we would look at first. Nothing is sent until you decide to send it.
Start the check
We tell you what is enforceable now and what is only direction of travel.
Every obligation gets tiered honestly, so your budget goes to the real ones first. You will not hear a deadline from us that we cannot point to in writing.
Who leads the work
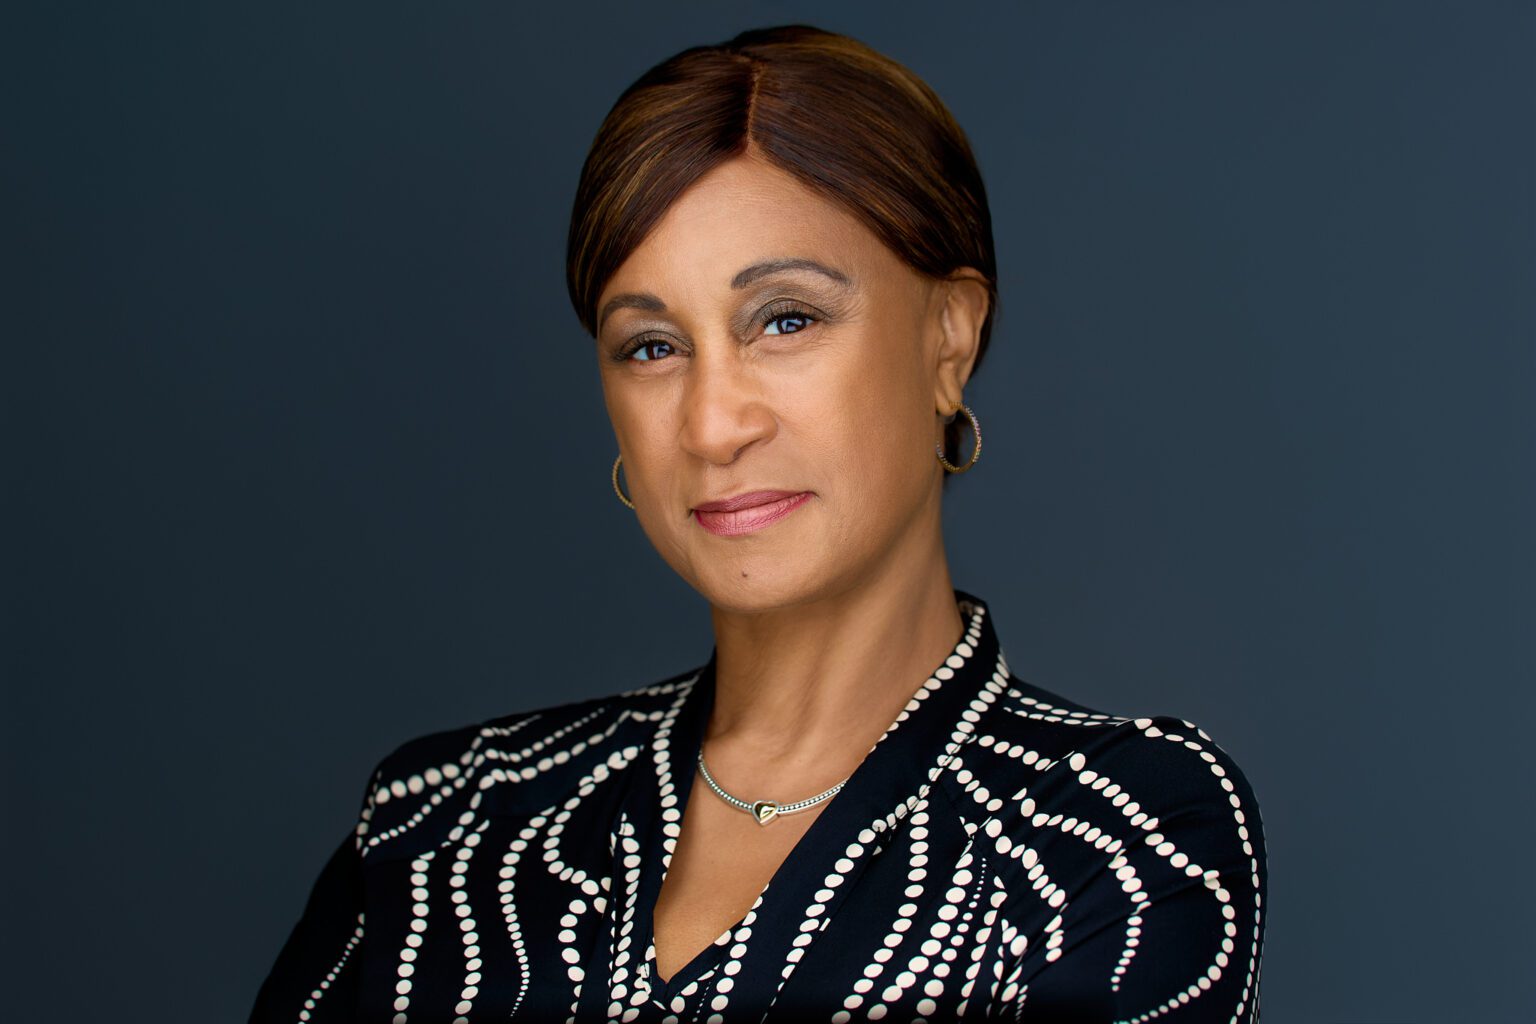
Nomad is led by Dr. Kimberly “KJ” Haywood, author of Here We Go Again… Except It’s AI: AI Governance from Analysis to Enterprise Action, supported by specialized consultants and executive board advisors across AI governance, cybersecurity, enterprise risk, compliance and business strategy.
Request an exposure review
A focused review of where your cyber and AI governance posture stands against the obligations enforceable today, with a red, yellow, green picture of what to address first.
No obligation, and you keep the findings either way. We reply within one business day.